 Definition
What is brute force protection in a CRM?
CRM brute force protection is a guard against someone trying one password after another until one works. Once too many attempts fail, the CRM stops accepting tries for a short time. In CIPHER CRM that pause shows up as a countdown on the sign-in screen, so the rightful owner can see when it ends.
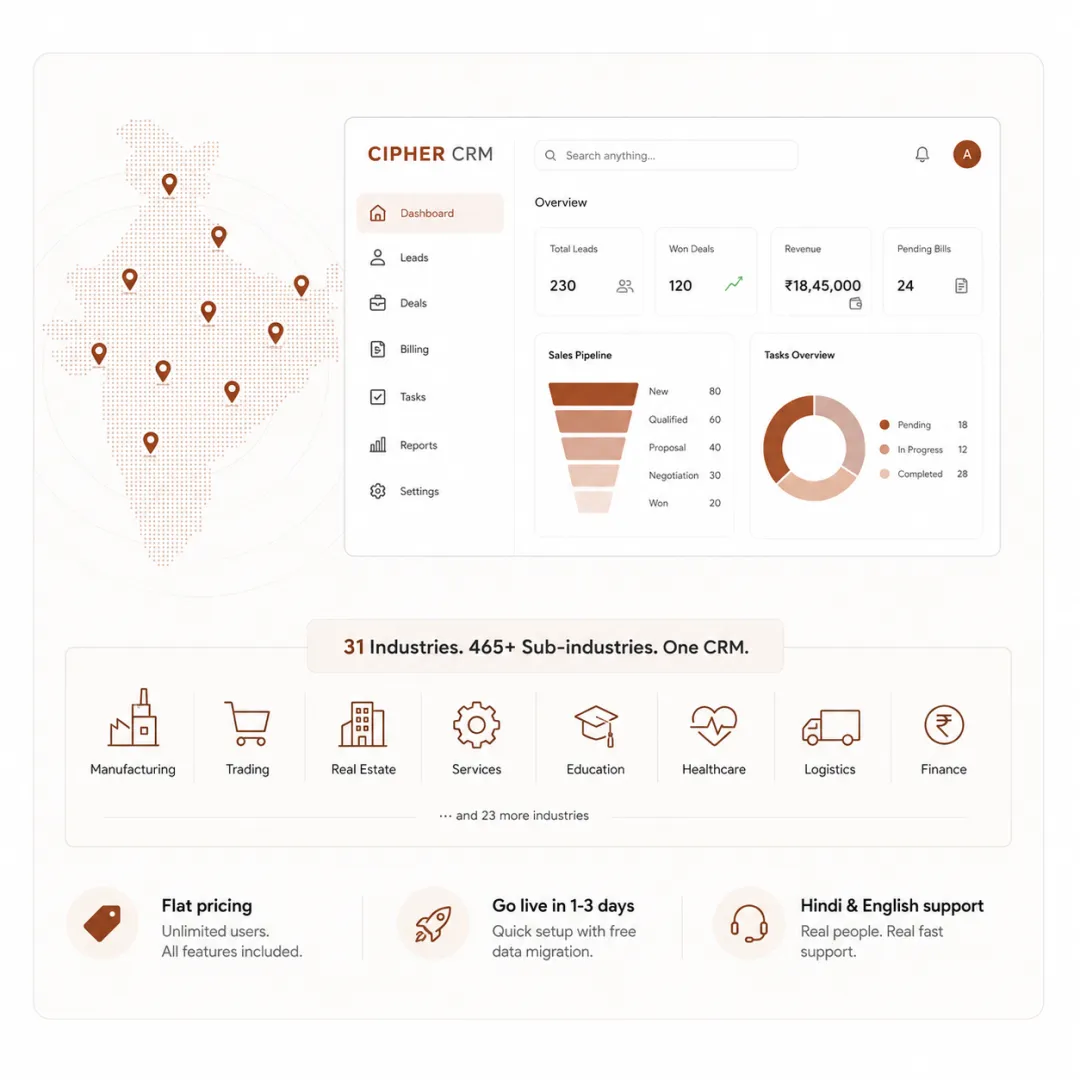
A brute-force attack is the simplest way to break into an account: keep guessing passwords until one fits. CIPHER CRM blocks this with a temporary lock. After repeated failed sign-in attempts, the account stops accepting new tries for a while, which turns fast guessing into a slow and hopeless job. The lock is not silent. A visible countdown appears on the sign-in screen, so a teammate who typed their password wrong a few times knows how long to wait instead of thinking the app is broken. When the countdown ends, sign-in opens again as normal. If someone has forgotten their password for good, they can reset it with a one-time emailed code. This protection is switched on for every account in every plan, with nothing to configure. CIPHER CRM is made by CIPHER Craft Pvt. Ltd. and used by 192+ businesses across 31 industries.
 The problem
 Capabilities
 How it works


 In action
 Compare


 Why it's worth it
 See how CIPHER CRM solves this


 Proof


 FAQ


 For your industry
 We're here to help


 Send on WhatsApp and get your demo
 No obligation
 Quick response
 Your data is safe