 Definition
What is role-based access control in a CRM?
Role-based access control means you give permissions to a role instead of to each person one by one. Everyone with that role gets the same access. In CIPHER CRM a role is a grid of View, Create, Edit and Delete switches across the areas of the CRM, and every staff member follows the grid of the role they hold.
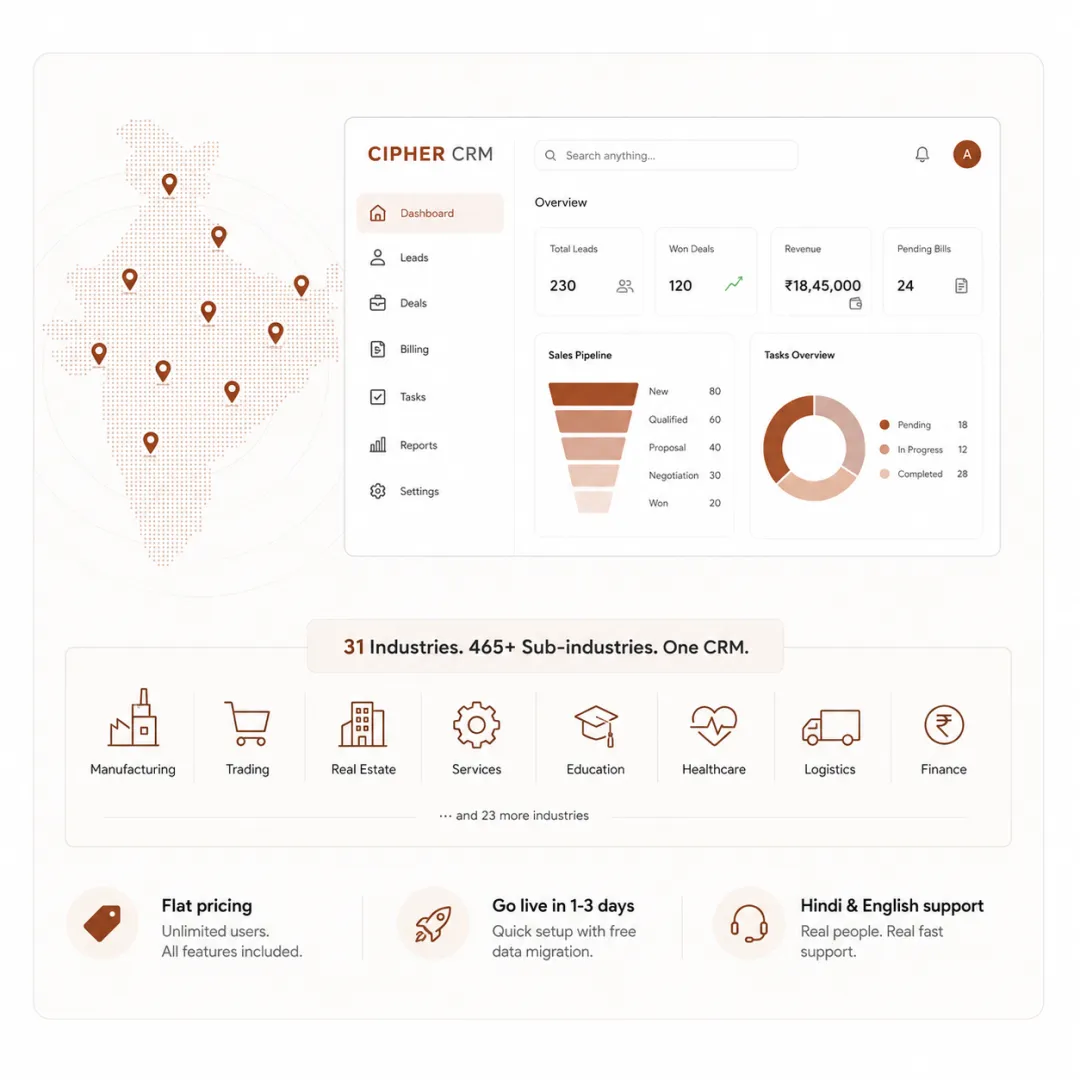
CIPHER CRM uses role-based access control to decide what each person can do. There are three access tiers. The Owner is one person per workspace. Admins have full access. Staff are governed by the Role they are given. Each role carries a permission matrix with four actions, View, Create, Edit and Delete, across roughly 30 feature areas: every record module such as leads, customers, projects, tasks and sales documents, every settings list such as lead statuses and sources, Chat and more. Bulk select-all and clear-all buttons make a new role quick to set up, and a live counter shows how many of the permissions in the grid are granted. Picking your industry during setup provides starter roles suited to your trade. Because access is set once per role, a new hire gets the right permissions the moment you give them a role. CIPHER CRM is used by 192+ businesses, rated 4.8 out of 5.
 The problem
 Capabilities
 How it works


 In action
 Compare


 Why it's worth it
 See how CIPHER CRM solves this


 Proof


 FAQ


 For your industry
 We're here to help


 Send on WhatsApp and get your demo
 No obligation
 Quick response
 Your data is safe